Trusted by enterprise security teams
PwC Trustwave Teachers Mutual Bank Swire Shipping Defense.com

What You Get When an Employee’s Credentials Leak

Each credential alert includes the leaked password or the stolen session cookie. The alert also shows where we found the credential, such as the stealer log’s file name or the phishing page’s URL.

Plaintext Passwords From Stealer Logs, Combo Lists and Phishing Kits

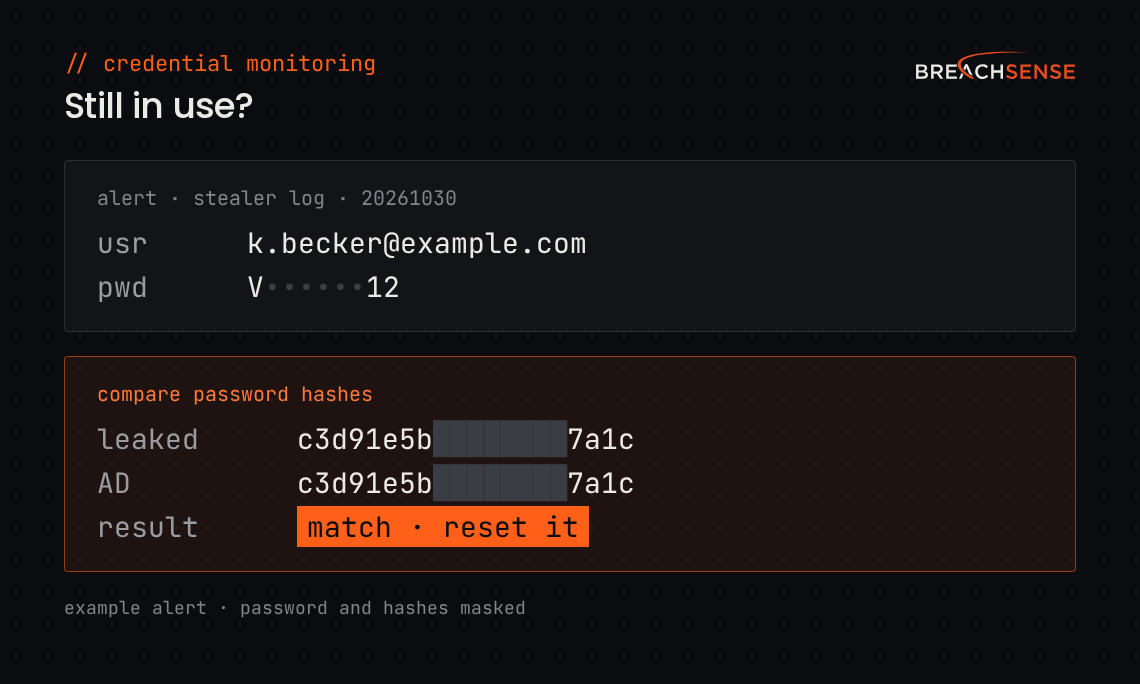
Because the alert includes the password exactly as the employee saved or typed it, you can check whether the employee still uses it. If you run AD (Active Directory), hash the leaked password the same way AD does. Then compare the result with the employee’s password hash in AD. A match means the leaked password is still the employee’s AD password. No match means the AD account doesn’t need a reset.

Once the employee has changed the password, add the leaked username and password pair to your whitelist. We then stop sending alerts for that pair.

Example stealer log alert for k.becker@example.com with a masked plaintext password, then the leaked password's hash compared with the hash Active Directory stores for k.becker. The two hashes match, so the employee still uses the leaked password

Session Tokens Returned as the Raw Cookie

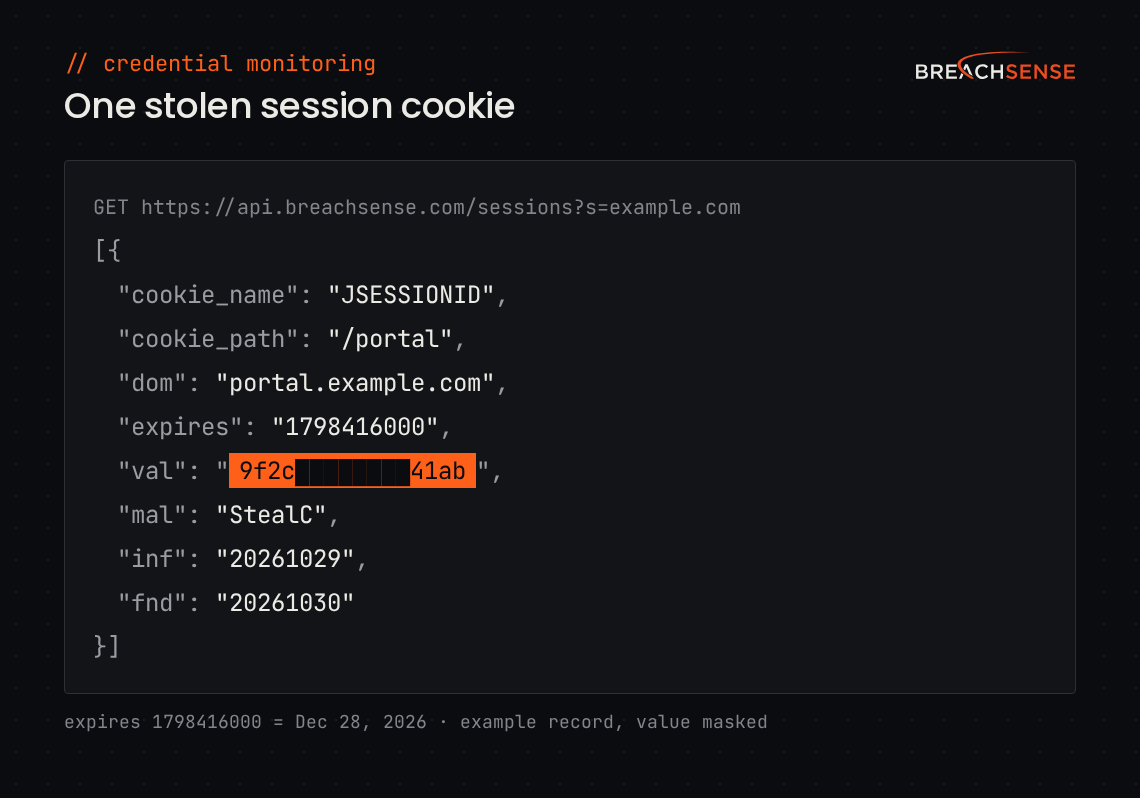
You can search our API for every stolen session cookie we find for your domains. Each cookie comes with its name, value, path and expiry date, so your team knows which session to revoke. In session hijacking, a stolen session cookie lets an attacker skip the password and MFA (multi-factor authentication) prompts.

You choose which session cookies to monitor by adding cookie names, such as example.com::JSESSIONID, to your watchlist. We send an alert when a cookie on your watchlist shows up in a stealer log. Start by revoking the sessions whose cookies haven’t expired yet. A password reset doesn’t always sign out other devices.

Example session cookie record from the Breachsense sessions endpoint for a JSESSIONID cookie on portal.example.com, showing the cookie name, the cookie path, the domain, the expiry date, a masked cookie value, the malware family StealC, the infection date and the date found

Every Other Account an Infected Employee Needs to Reset

In every one of our monthly infostealer reports, the median infected machine leaked 19 or more saved passwords. A quarter of the machines leaked more than 60 saved passwords.

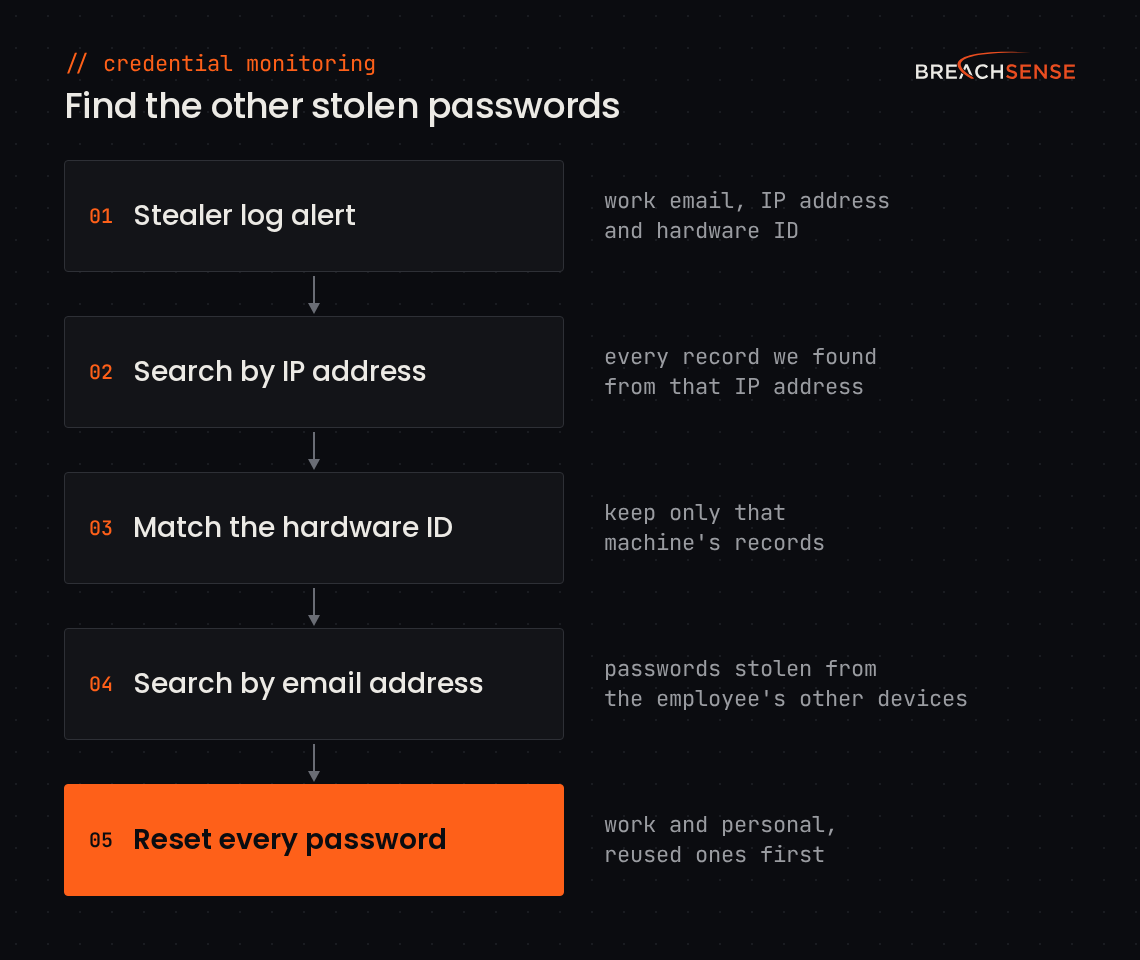
Stealer log alerts can include the infected machine’s IP address and hardware ID. Search our API by that IP address to find the employee’s other stolen passwords. The results list every credential we found in stealer logs from that IP address, including passwords for personal accounts. With NAT (network address translation), every device on a network shares one public IP address, so the results can include credentials from other machines. Keep the records with the same hardware ID as the alert to narrow the results to the infected machine. A search by the employee’s email address also finds credentials saved under that address on their other infected devices.

Have the employee change every password these searches found, starting with any personal password the employee also uses at work.

Five-step flow: a stealer log alert with a work email, IP address and hardware ID; a search by that IP address; the results narrowed to the alert's hardware ID; a search by the employee's email address for passwords stolen from other devices; then every work and personal password reset, reused ones first

What is Credential Leak Monitoring?

Credential leak monitoring, also called credential monitoring, continuously searches stealer logs, combo lists, phishing kits and third-party breaches for your employees’ leaked passwords and session tokens. We crack hashed passwords from third-party breaches where we can.

We also index the full contents of leaked files from ransomware attacks and third-party breaches, plus unsecured databases. You can search the leaked files and databases for any term, such as your company name or an internal project code name.

If you’re still comparing vendors, our credential monitoring software roundup shows what each of 10 tools includes in an alert, such as a plaintext or hashed password and stolen session cookies.

Where Breachsense Finds Leaked Credentials

Credentials From Stealer Logs

We index new stealer logs within hours. The infected device can be a home computer your security tools don’t cover. Clean or reimage that device before the employee resets their passwords. The login URL in each record shows which system the password is for, such as your VPN or a SaaS app. With infostealer detection, we also send alerts when stealer logs contain session cookies you monitor or your API keys.

Credentials Typed Into Phishing Kits

When we find an employee’s password in a phishing kit, the employee typed it into a fake login page. Most phished passwords aren’t in any breach data, so a tool that only monitors third-party breaches and combo lists won’t find those passwords. The alert includes the phishing page’s URL, so you can block the page and warn other employees. If the employee typed a one-time MFA code into the fake page, the alert includes that code too. A code in the alert means the attacker got past MFA, so revoke the employee’s sessions and reset the password.

Combo Lists Built for Credential Stuffing

Combo lists are username and password pairs packaged for credential stuffing. Attackers compile combo lists from old third-party breaches and stealer logs, then trade the lists on hacker forums and Telegram channels. When a combo list contains an employee’s email address, we send an alert with the plaintext password. If the employee still uses that password, have them change it on every site where they used it.

Third-Party Breaches and Leaked Files

We crack the password hashes from other sites’ breaches to plaintext where we can. Third-party breach monitoring also covers breaches at your vendors. When a vendor is hit by ransomware, its leaked files can contain your employees’ credentials and your company’s data. When a leaked file contains a term you monitor, such as your domain or a project name, we send an alert with the file’s URL. If the file later goes offline, you can download its extracted text from our backup.
SourceWhat a match meansWhat the record includes
Stealer logsMalware on a device copied the saved passwordUsername, plaintext password, login URL and date found. The malware family, infection date, IP address and hardware ID when the stealer log contains them
Phishing kitsThe employee typed the password into a fake login pageUsername, plaintext password, phishing page URL and date found. The impersonated brand, if the kit recorded it
Combo listsAttackers are sharing the pair for credential stuffingUsername, plaintext password, file name and date found
Third-party breachesA third-party site's database leaked the employee's password for that site. The employee may use the same password on your networkEmail address, password (cracked to plaintext where we can), breached site and date found

Who Uses Credential Leak Monitoring?

Security operations, MSSPs (managed security service providers), IT and identity teams use credential leak monitoring.

  • SECOPS

    SecOps team monitoring a single brand

    Get alerts when an employee's password or a session cookie you monitor shows up in a stealer log. We can send each alert by webhook to your SIEM (security information and event management) or IAM (identity and access management) tools.

    What they use:
    Domain monitoringinfostealer logssession token alertsSIEM webhook
  • MSSP / MSP

    MSSP monitoring multiple clients

    Run credential monitoring across a client portfolio with a separate watchlist and webhook route for each client. Your ticketing tool can then file each alert in the right client's queue.

    What they use:
    MSP monitoringper-domain webhook routingper-client watchlists
  • IT

    IT teams without a dedicated security role

    Add your domains to the watchlist once. We email you when we find an employee's leaked credentials.

    What they use:
    Email alertsthe dark web scandomain monitoring
  • IDENTITY / IAM

    Identity and IAM teams

    Catch stolen session tokens that bypass your MFA. Send each alert to your own automation, which can revoke the user's sessions.

    What they use:
    Session token detectionwebhook alertswebhook-driven revocation
How Does Breachsense Detect Leaked Credentials?

Your tools can search leaked files and pull credentials from our API. Or run the same searches in plain English from Claude Code, Codex or GitHub Copilot.

Add Domains & Employee Emails

Add your company domains, plus any personal email addresses you want to monitor, such as your executives’. Monitoring example.com covers every email address ending in @example.com.

We Scan Stealer Logs & Breaches

We check new stealer logs, combo lists, phishing kits and third-party breaches against your watchlist.

Get Credential Alerts Via Email or Webhook

When a credential matches your watchlist, we email an alert to your inbox or send it by webhook to your SIEM or SOAR (security orchestration, automation and response) tool. Your SOAR can then reset the password and revoke the session.

Reset Passwords Fast

Your team or a SOAR playbook resets the leaked password and revokes the user’s sessions.

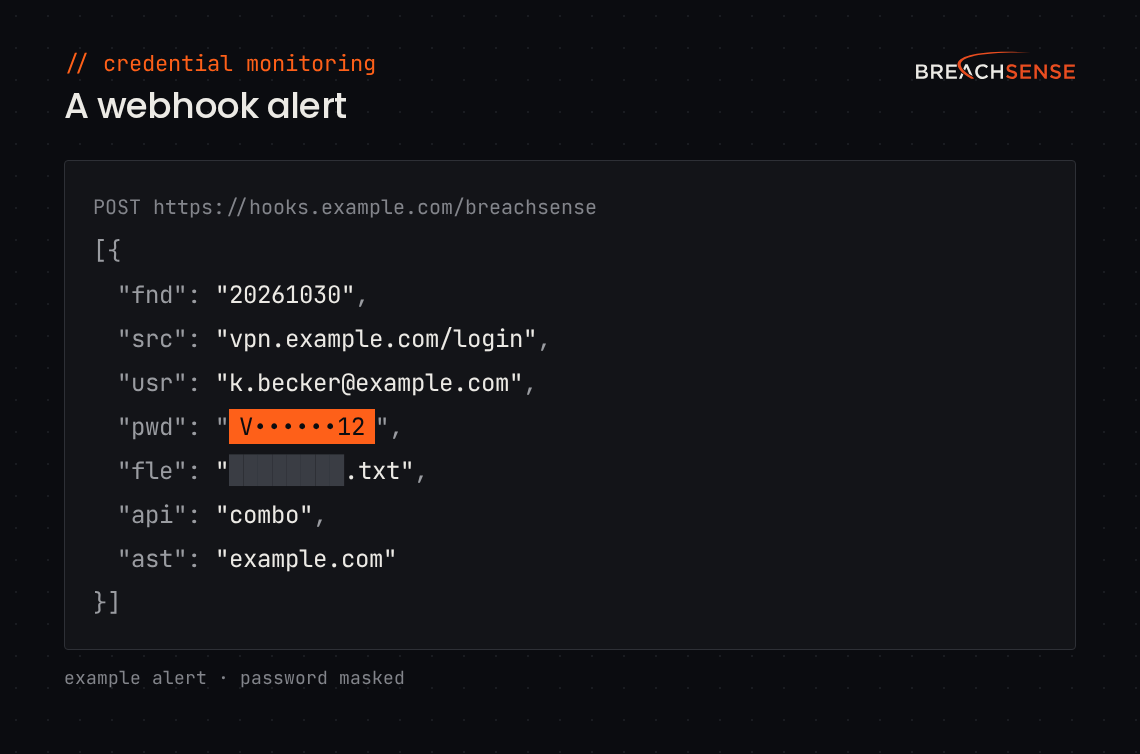
Example Breachsense webhook alert in JSON for a combo list credential, showing the date found, the login URL, the username k.becker@example.com, a masked password, a redacted file name, the endpoint and the monitored domain example.com

Frequently Asked Questions

Compromised credentials are usernames, passwords and session tokens that an attacker has used to get into an account. A leaked credential becomes compromised once an attacker starts using it.
Infostealer malware copies the passwords saved in an employee’s browser, including work passwords saved on a home computer. A breached website leaks employees’ passwords for that site, which some reuse at work. Phishing pages trick employees into typing their passwords, a technique called credential harvesting. Attackers sell the credentials on dark web marketplaces and package them into combo lists.
Leaked credentials are exposed but not necessarily being used by attackers yet. Compromised credentials are actively being exploited. Credential leak monitoring finds leaked credentials so you can reset the password before an attacker uses it.
Attackers can use stolen credentials as soon as they get them. Automated tools test stolen username and password pairs against many sites at once in credential stuffing attacks. Infostealer malware can also steal session cookies, which let an attacker skip MFA. When an alert includes a stolen cookie, revoke the session and reset the password.
If infostealer malware took the credentials, clean or reimage the infected device first, because the malware can steal the new password too. If the employee still uses the leaked password, reset it and revoke their sessions. Check sign-in logs for access since the leak. Then have the employee change every other password saved on that device.
Breachsense collects leaked credentials from stealer logs, combo lists, phishing kits and third-party breaches, among other sources we track. We crack hashed passwords to plaintext where we can. When a leaked credential matches your watchlist, we send an alert by email or webhook.

Credential Security Resources

Dark Web Monitoring

Track criminal marketplaces and hacker forums where stolen credentials are sold. Detect leaked passwords before they’re used to breach your systems.

Learn More

Leaked Credentials Detection

Learn how to detect leaked credentials across dark web sources and stealer logs before they’re used against you.

Learn More

What Are Compromised Credentials?

Understand how credentials become compromised and the difference between leaked and actively exploited credentials.

Learn More

Credential Stuffing Attacks

Learn how attackers use leaked credentials in automated credential stuffing attacks. Understand the attack methodology and how to defend against it.

Learn More

Dark Web Credential Monitoring Tools

Compare 10 credential monitoring tools on where they find leaked passwords and what each alert contains.

Learn More

Password Breach Guide

Full guide to understanding password breaches. Learn how passwords get compromised and what to do when your credentials are exposed.

Learn More

Malware Incident Response

How to respond when infostealer malware compromises employee devices and harvests credentials.

Learn More

Detect Leaked Credentials Before Attackers Strike

Book a demo